 Baku 17° C
CBA official urges financial institutions to regularly test cyber resilience
- 28 October, 2026
- 16:35
Stay up to date with the top news!
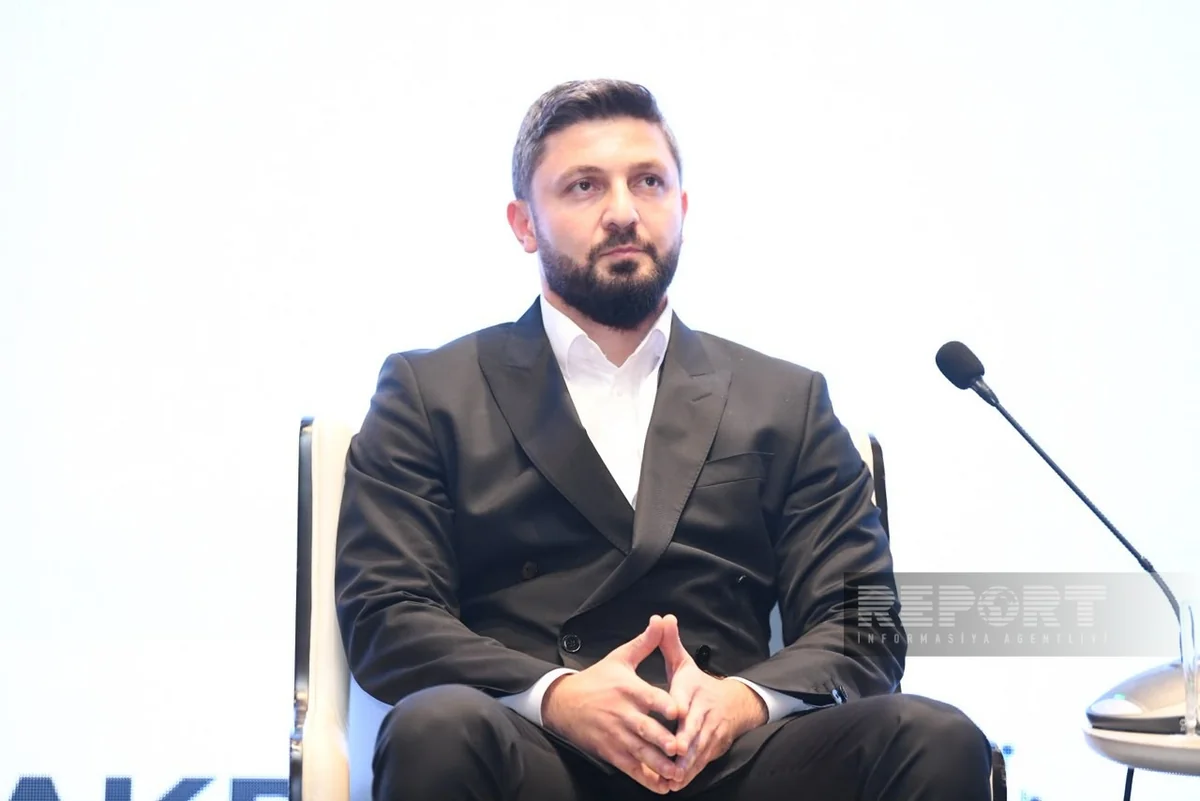
Systems should be audited again after cybersecurity incidents, and the effectiveness of information security measures should be assessed regularly, said Abid Alasgarzada, deputy director of the Central Bank of Azerbaijan's Information and Cybersecurity Department.
Report informs that he was speaking at the 12th Investment and Sustainable Development in Microfinance Conference, organized by the Azerbaijan Microfinance Association (AMFA) in Baku.
According to Alasgarzada, passing an audit alone is insufficient to protect against cyberthreats. An audit assesses an organization's information security at a particular point in time, while system resilience and the effectiveness of security measures require ongoing testing.
"An audit covers a specific period-a particular point in time-and shows the organization's condition at that time. However, information security maturity and resilience must be assessed regularly. An audit is not the final step that completes this process," he said.
Under the Central Bank's information security regulations, Category 1 entities must have their information security management systems (ISMS) audited and assessed annually by an internationally accredited auditor. Category 2 and Category 3 entities, including nonbank credit institutions, must undergo such assessments at least once every two years.
Alasgarzada emphasized that engaging an internationally accredited auditor does not guarantee that an organization will avoid future cyberthreats. Alongside documentation, the practical implementation of security measures and readiness to respond to potential incidents are therefore essential.
He illustrated this with the example of backups. Even if an organization passes an audit and maintains proper backup documentation and information security policies, this does not guarantee that its systems can be restored following an attack.
"Suppose an organization suffers a ransomware attack and its files are encrypted. The Central Bank requires backups to be stored in a separate environment. However, the organization has failed to meet this requirement and has not protected its backups against encryption. As a result, a serious incident occurs, causing major operational problems," he said.
Conversely, an organization that stores backups securely and regularly tests their restoration can recover from such attacks with fewer losses, Alasgarzada said. The Central Bank's requirements also stipulate that restoration from backups must be tested twice a year.
He said compliance would allow organizations to restore systems from backups and resume operations even if a cyber incident causes a temporary disruption.
Alasgarzada added that organizations' obligations following a cybersecurity incident extend beyond reporting it. Existing security policies must be reviewed, and organizations must identify which parts of the affected systems require another internal or external audit.
He also stressed the importance of management's involvement in post-incident measures. Existing requirements call for engagement at the Supervisory Board level, while the person responsible for information security must report directly to the Supervisory Board.
"This is an area in which management must take a direct interest," he said.
Author